If you’re searching for static code analysis tools, this roundup compares seven books and guides rather than software products. My best overall pick is Static Analysis Engineering for its focus on finding defects before release; MISRA C & CERT C Made Practical is the more targeted choice for embedded C, while Auditing Source Code connects analysis with Linux security and patching. The main tradeoffs are breadth versus specialization, practical workflow advice versus technical depth, and general guidance versus language-specific rules. These titles can help you choose and apply analysis methods, but they are not themselves analyzers or substitutes for checking current tool support. Read on for the full breakdown and a guide to matching a book to your team’s needs.

Get business pricing on monitors, keyboards and dev gear
- Business-only prices and quantity discounts
- Tax-exempt purchasing
- Multiple users, one account, clear invoices
Key Takeaways
- Static Analysis Engineering leads for general defect-prevention learning because its focus is identifying problems before production, rather than on a single language or tool.
- Auditing Source Code is the strongest fit for Linux security work, where static analysis needs to sit alongside source auditing and vulnerability patching.
- MISRA C & CERT C Made Practical is the clearest specialist option for embedded C teams that need to connect coding rules with analysis practice.
- Program Analysis and Optimization in Static Compilers offers a more technical route into flow analysis and symbolic execution, but its compiler emphasis is less relevant to everyday tool selection.
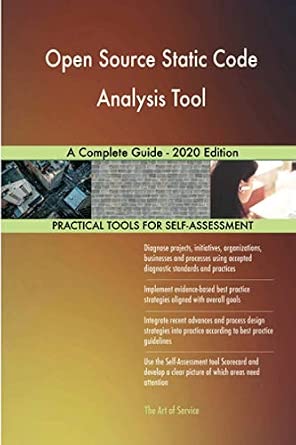
- Open Source Static Code Analysis Tool: A Complete Guide – 2020 Edition may suit readers seeking an introductory open-source angle, but its 2020 date makes checking current tooling guidance especially important.



| static code analysis tool | Subject | Topic | Format |
|---|---|---|---|
| Auditing Source Code: Automate | — | Software security | — |
| Static Analysis Engineering: D | Static analysis engineering | — | Book |
| Program Analysis and Optimizat | Program analysis and optimization | Flow analysis | — |
| Comparison of Fagan Inspection | Fagan inspections and static code analysis | — | Book |
| Open Source Static Code Analys | Open-source static code analysis tools | — | — |
| Code Review Intelligence: Chan | Code review intelligence | — | Book |
| MISRA C & CERT C Made Practica | — | — | Book |
More Details on Our Top Picks
Auditing Source Code: Automated Testing, Static Analysis, and Vulnerability Patching for Linux Software
Linux-specific security guidance gives this book a practical angle for teams auditing software in that environment. It connects static analysis with automated testing and vulnerability patching, helping readers place findings within a broader remediation process rather than treating tool output as the finish line. Compared with Static Analysis Engineering: Detecting Software Defects Before They Reach Production, whose supplied description centers on defect detection, this title has a clearer security and platform focus. That focus is also its main limitation: its advice may not transfer cleanly to teams working across other operating systems, and the technical material may be difficult for newcomers. I would choose it for Linux security work, not as a general introduction to static analysis or a guide to choosing tools across platforms.
Pros:- Combines static analysis with automated testing and vulnerability patching.
- Focuses specifically on Linux software environments.
- Offers practical guidance on implementing secure coding standards.
Cons:- Technical content may be challenging for readers new to software security.
- Linux emphasis limits its usefulness for teams working primarily on other platforms.
Best for: Linux developers and security practitioners who want to connect static analysis findings with testing, secure coding practices, and vulnerability remediation.
Not ideal for: Beginners seeking a gentle introduction, or teams needing guidance that applies equally to Windows, macOS, and cross-platform projects.
- Topic:Software security
- Platform:Linux
- Focus area:Static analysis
- Focus area:Automated testing
- Focus area:Vulnerability patching
- Guidance:Secure coding standards
Our verdict“Choose this book for Linux-focused security auditing that ties static analysis to testing and remediation, but skip it for broad, beginner-oriented tool guidance.”
Static Analysis Engineering: Detecting Software Defects Before They Reach Production
The title’s strongest distinction is its production-focused framing: static analysis is presented as a way to catch defects before release, which makes it a natural fit for teams looking to move checks earlier in development. Compared with Auditing Source Code: Automated Testing, Static Analysis, and Vulnerability Patching for Linux Software, it appears less tied to security auditing or a particular operating system and more centered on general defect prevention. That broader promise could suit engineering teams, but the available description gives no details about languages, tools, workflows, or technical depth. I would treat it as a topic-led choice rather than a confirmed implementation manual. Readers who need specific tool comparisons or hands-on configuration steps may find the lack of detail a meaningful limitation.
Pros:- Centers static analysis on preventing defects before production.
- Has a clear software engineering focus.
- The title suggests relevance to teams interested in earlier defect detection.
Cons:- Available product information does not identify tools, languages, or supported workflows.
- The depth and practical detail cannot be established from the supplied description.
Best for: Engineering leads and developers seeking a resource focused on catching software defects through static analysis before production.
Not ideal for: Readers who need verified coverage of specific tools, programming languages, configuration steps, or Linux security practices.
- Subject:Static analysis engineering
- Primary focus:Detecting software defects
- Intended timing:Before production
- Format:Book
- Programming languages:Not specified
- Tools covered:Not specified
Our verdict“Consider it for a defect-prevention-oriented reading list, but choose a more fully specified guide if you need concrete tool or workflow instructions.”
Program Analysis and Optimization in Static Compilers: Flow Analysis, Symbolic Execution, and Performance Diagnostics
Flow analysis, symbolic execution, and performance diagnostics give this title a more technical, compiler-centered scope than the other books in this group. It is the clearest fit for readers who want to understand analytical methods behind static compilers, rather than simply evaluate a development-team tool. Compared with Open Source Static Code Analysis Tool: A Complete Guide – 2020 Edition, this book’s stated focus is on program analysis and optimization concepts, not open-source tool selection. That makes it a potentially stronger match for compiler-oriented study, but a less direct route to setting up everyday code checks. The supplied details do not specify languages, examples, or implementation coverage, so readers seeking a practical adoption guide should verify that it matches their needs before choosing it.
Pros:- Names flow analysis as a core subject.
- Covers symbolic execution, a distinct program-analysis technique.
- Includes performance diagnostics and compiler optimization in its stated scope.
Cons:- Compiler and optimization focus may be too specialized for routine code-review needs.
- Available details do not specify languages, examples, or practical tool setup.
Best for: Compiler developers, computer science students, and experienced engineers studying flow analysis, symbolic execution, or static optimization.
Not ideal for: Teams seeking a straightforward guide to selecting and deploying static analysis tools in a standard application development workflow.
- Subject:Program analysis and optimization
- Context:Static compilers
- Topic:Flow analysis
- Topic:Symbolic execution
- Topic:Performance diagnostics
- Programming languages:Not specified
Our verdict“Pick this for compiler-oriented study of analysis techniques, not as a first-choice manual for adopting team-wide static analysis tools.”
Comparison of Fagan Inspections and Static Code Analysis Tools (German Edition)
This book’s distinguishing feature is its comparison of Fagan inspections with tool-supported static analysis. That makes it relevant to readers weighing human review practices against automated checks, rather than to someone simply looking for a tool tutorial. Unlike Static Analysis Engineering: Detecting Software Defects Before They Reach Production, which is framed around catching defects before release, this title explicitly sets static analysis beside a named inspection method. Its German-language edition narrows the audience, and the supplied information does not say which tools, evaluation criteria, or project settings the comparison covers. I would select it for a German-speaking reader interested in review-process choices, but not for buyers who need a current, hands-on guide to configuring analyzers or integrating them into a build pipeline.
Pros:- Directly compares Fagan inspections with static code analysis.
- Addresses both human review and tool-supported analysis.
- Provides a German-language option on software quality processes.
Cons:- German language limits accessibility for readers who do not read German.
- Available details do not identify tools, comparison criteria, or implementation guidance.
Best for: German-speaking software engineering students, quality managers, and team leads comparing formal inspections with automated static analysis.
Not ideal for: Readers who need English-language material or practical instructions for configuring current analysis tools and development pipelines.
- Subject:Fagan inspections and static code analysis
- Format:Book
- Language:German
- Comparison focus:Formal inspections versus tool-supported analysis
- Specific tools:Not specified
- Implementation guidance:Not specified
Our verdict“Choose this for a German-language comparison of inspection and analysis approaches, not for hands-on tool adoption guidance.”
Open Source Static Code Analysis Tool: A Complete Guide – 2020 Edition
Open-source static analysis is the central appeal here: the guide is framed around tools and methods that can support development workflows without relying on proprietary options. Compared with Program Analysis and Optimization in Static Compilers, which focuses on analysis techniques inside compiler and optimization contexts, this title appears more directly aimed at tool adoption. Its 2020 edition date is the key tradeoff. Static analysis tools and their integrations change, so advice about specific recommendations may no longer reflect current capabilities. The supplied description also does not name tools or programming languages, which makes it hard to judge how actionable the guide is for a particular codebase. I would use it for historical or foundational orientation, then check current tool documentation before making implementation choices.
Pros:- Focuses on open-source static analysis tools.
- Frames the material around methods and development workflow implementation.
- Offers a tool-adoption angle distinct from compiler-theory-focused material.
Cons:- The 2020 edition may not reflect current tool features or recommendations.
- Available details do not name the tools, languages, or integrations covered.
Best for: Developers and small engineering teams exploring open-source static analysis approaches and seeking a starting point for workflow planning.
Not ideal for: Teams selecting tools for a current production pipeline who need up-to-date recommendations, language coverage, or current integration instructions.
- Subject:Open-source static code analysis tools
- Edition:2020
- Focus:Methods and best practices
- Application:Software development workflows
- Tool licensing focus:Open source
- Specific tools:Not specified
Our verdict“Use it as an introductory reference for open-source analysis workflows, but verify tool recommendations against current documentation.”
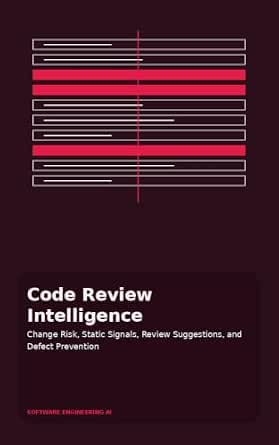
Code Review Intelligence: Change Risk, Static Signals, Review Suggestions, and Defect Prevention
Code Review Intelligence is aimed at teams that want static signals to shape review priorities, not just flag issues after a change is made. Its focus on change risk and automated suggestions can help reviewers direct attention toward modifications more likely to introduce defects. Compared with Static Analysis Engineering: Detecting Software Defects Before They Reach Production, this book appears more centered on review decisions and actionable feedback than on the broader practice of defect detection. That narrower focus is useful when review capacity is tight, but the description does not identify supported languages, tools, or integration methods, so buyers cannot judge how directly its approach fits their workflow. I’d choose it for process guidance, not as a substitute for a named analyzer or implementation manual.
Pros:- Focuses on identifying high-risk changes early in review
- Connects static signals with review decisions
- Offers automated review suggestions aimed at defect prevention
Cons:- The description does not name supported languages, analysis tools, or integrations
- No specific user feedback is available to help judge the clarity or depth of the guidance
Best for: Engineering leads and code reviewers who want to prioritize risky changes and make review feedback more actionable.
Not ideal for: Developers seeking setup instructions for a specific static analysis tool, language, or CI integration, since those details are not provided.
- Format:Book
- Subject:Code review intelligence
- Analysis focus:Change risk and static signals
- Stated goal:Defect prevention
- Specific languages or tools:Not specified
Our verdict“Choose this for risk-focused review process guidance, but skip it if you need tool-specific implementation instructions.”
MISRA C & CERT C Made Practical: Hands-On Static Analysis and Safer Embedded C Programming for Developers
MISRA C & CERT C Made Practical is the most specialized choice here: it brings static analysis into the context of safer embedded C and established coding standards. Its hands-on framing makes it a better fit for developers who need to apply MISRA C or CERT C practices than Code Review Intelligence, which focuses on change risk and review suggestions rather than embedded-language compliance. That specificity is also the main limitation. General application developers, or teams working outside C, may get little from a standards-centered guide, and the provided description does not name analyzers or give evidence about the depth of its exercises. I’d shortlist it when embedded C standards are part of the job; for broader static analysis concepts, a general text in the roundup is a closer match.
Pros:- Targets embedded C developers rather than treating all languages alike
- Focuses on practical application of MISRA C and CERT C
- Covers hands-on static analysis techniques
- Connects coding standards with safer programming practices
Cons:- Its standards and language focus may not transfer well to general software teams
- The description does not identify specific analysis tools or detail the exercises
- No customer feedback is available to help assess clarity
Best for: Embedded C developers and technical leads applying MISRA C or CERT C rules and static analysis in safety-conscious software work.
Not ideal for: General-purpose programmers and teams working primarily in languages other than C, since the guide is focused on embedded C standards.
- Format:Book
- Primary language focus:C
- Target domain:Embedded software
- Coding standards:MISRA C and CERT C
- Analysis approach:Hands-on static analysis
- Stated programming goal:Safer embedded C programming
Our verdict“Choose this if MISRA C or CERT C governs your embedded work; choose a broader static analysis guide for cross-language needs.”
How We Picked
I ranked these seven titles by how directly they help a buyer understand, select, or apply static analysis. The main criteria were practical relevance, clarity of audience, usefulness for real development workflows, and the specificity of the subject matter. I also considered whether a title focuses on defect prevention, security auditing, compiler techniques, code review, or standards-driven embedded development, since those needs call for different resources.
Static Analysis Engineering ranks first as the broadest match for readers seeking a foundation in finding defects before release. More specialized titles follow when their focus offers a clear advantage for a particular team, while the German comparison and dated open-source guide rank lower for readers looking for broadly applicable, current implementation guidance. These are books and guides, not executable analyzers; I have not treated them as software products or inferred features beyond their stated titles.
| static code analysis tool | Topic | Subject |
|---|---|---|
| Auditing Source Code: Automate | Software security | — |
| Static Analysis Engineering: D | — | Static analysis engineering |
| Program Analysis and Optimizat | Flow analysis | Program analysis and optimization |
| Comparison of Fagan Inspection | — | Fagan inspections and static code analysis |
| Open Source Static Code Analys | — | Open-source static code analysis tools |
| Code Review Intelligence: Chan | — | Code review intelligence |
| MISRA C & CERT C Made Practica | — | — |
Factors to Consider When Choosing Static Code Analysis Tools
Choosing a learning resource for static analysis starts with the problem your team needs to solve, not with the word “analysis” on a cover. I’d match the title to your language, risk profile, and the decisions you need to make after a tool reports an issue. These broader checks can help prevent buying a technically interesting book that does little for your day-to-day workflow.
Match the material to your language and risk profile
Static analysis concepts travel across languages, but rule sets and failure modes do not. A general engineering resource can explain how to reason about defects, while embedded C teams may need standards-specific guidance that connects rules to coding practice. Security-focused Linux work has different priorities again, including vulnerability review and remediation. A common mistake is choosing a broad title when the immediate need is a language-specific compliance process. Before choosing, write down the languages, safety or security requirements, and typical defects your team handles. Pay for specialization only when those details are central to the work.
Separate tool-selection advice from analysis theory
Some resources help readers understand analysis techniques; others are better suited to choosing or integrating an analyzer. Theory can clarify why data flow, symbolic execution, or compiler diagnostics reveal certain defects, but it may not answer questions about editor support, CI integration, or team workflows. If you need to shortlist software, look for current documentation and trials alongside any book. Avoid treating a conceptual guide as a feature comparison for tools that may have changed since publication. For foundational learning, technical depth can be worthwhile even when it does not provide a ready-made procurement checklist.
Check publication date against fast-moving tool ecosystems
Static analysis principles can remain useful for years, while product interfaces, language versions, and open-source project health can change quickly. A dated guide may still explain durable concepts, but examples of supported tools or setup steps can be stale. Check the publication date, then verify any named analyzer’s current maintenance status and compatibility with your codebase. This matters especially when a book presents itself as a guide to a particular generation of open-source tools. If your goal is immediate implementation, current vendor and project documentation should carry more weight than an older overview.
Decide whether your gap is technical or organizational
A team may understand how an analyzer reports defects yet still struggle with triage, ownership, and keeping warnings actionable. Technical books tend to explain analysis methods; code-review and change-risk material may better support decisions about where findings fit into review. These are related but distinct needs. Before buying, ask whether developers need help interpreting reports, reviewers need stronger risk signals, or leads need a rollout process. Choosing a book for the wrong gap can leave the real bottleneck untouched. If adoption is the challenge, prioritize material that discusses workflow and defect prevention, not only analysis mechanics.
Look for a path from findings to action
Finding a defect is only useful if the team can judge its severity, assign responsibility, and resolve it without overwhelming developers. When comparing resources, look for coverage of false positives, prioritization, suppressions, and remediation habits—not just the analyzer’s ability to produce findings. A common rollout mistake is enabling every rule at once and flooding a project with warnings. A staged approach, starting with high-confidence findings or changed code, can make adoption easier to sustain. If a book emphasizes detection but says little about acting on results, pair it with practical workflow guidance.
Choose depth that fits the reader
A specialist treatment of compiler analysis can be valuable for researchers or tool developers and frustrating for readers who need a first introduction. Conversely, an introductory guide may not satisfy engineers working on complex data-flow or optimization problems. Consider who will read the material and what they already know before choosing a technical level. For mixed-experience teams, a broad foundation can support shared vocabulary, with specialist references added for particular projects. Paying for depth makes sense when readers will apply it; otherwise, a focused, accessible resource may deliver more practical value.
Frequently Asked Questions
Are these titles software tools I can install?
No. The seven items in this roundup are books or guides about static analysis, code auditing, compiler techniques, code review, or coding standards. They do not scan a repository or integrate into a build on their own. If you need an analyzer, use these resources to shape your requirements, then evaluate actual software against your languages, CI setup, and security needs. Confirm current capabilities directly with the tool’s documentation.
Which book should I choose if my team has not used static analysis before?
Static Analysis Engineering is the broadest starting point in this group because its stated focus is detecting defects before production. It is a better general foundation than compiler-centered material if your aim is to understand why teams analyze code and how defects can be caught earlier. Readers who work only with embedded C may get more immediate relevance from the MISRA and CERT guide. Pair any book with a small trial on a real project so the team can connect concepts to its own findings.
Is the 2020 open-source guide still useful for choosing an analyzer?
It may help with introductory concepts or give readers a starting point for understanding open-source analysis, but its date calls for caution. Tool maintenance, language support, integrations, and recommended practices can change after publication. Treat the book as background rather than a current catalog or final buying authority. Check the latest project documentation and release activity for any analyzer it discusses before adopting it.
Should an embedded C team choose a standards guide or a general static-analysis book?
If the team’s immediate work involves MISRA C or CERT C practices, the standards-focused guide is the more direct match. A general analysis book can still help explain broader defect-detection concepts, but it may not address the rules and constraints that shape embedded development. Consider whether your challenge is understanding analysis overall or applying coding standards consistently. Teams with both needs may benefit from a general foundation plus a focused standards reference rather than expecting one title to cover everything.
Can a book about static analysis replace a tool evaluation or compliance review?
No. A book can clarify methods, terminology, and possible workflows, but it cannot confirm that a particular analyzer supports your codebase or meets an organization’s requirements. Tool evaluation should include representative code, integration checks, finding quality, and the team’s capacity to handle reports. Compliance decisions also depend on the applicable standard, project rules, and evidence required by the organization. Use reading to prepare better questions, then validate answers against current software and project-specific requirements.
Conclusion
For the strongest general learning choice, I recommend Static Analysis Engineering as best overall because its defect-prevention focus fits readers across a range of teams. The best value in breadth is also the practical starting point for readers who want one general foundation rather than a specialist reference; those who need an open-source introduction can look at the 2020 guide, while verifying all tool details against current sources. For best premium-level technical depth, choose Program Analysis and Optimization in Static Compilers if compiler methods, flow analysis, or symbolic execution are central to your work. Beginners should start with the general engineering focus, while embedded C teams should prioritize MISRA C & CERT C Made Practical. Choose Auditing Source Code for Linux security and patching, and Code Review Intelligence when change risk and review signals are the main concern; the German comparison is most relevant to readers specifically seeking that comparison in German.
Fall Picks
fall essentials
As an affiliate, we earn on qualifying purchases.