TL;DR
Open a free Amazon Business account
Business pricing, bulk buying and tax-exempt orders.
Create a free accountAs an affiliate, we earn on qualifying purchases.
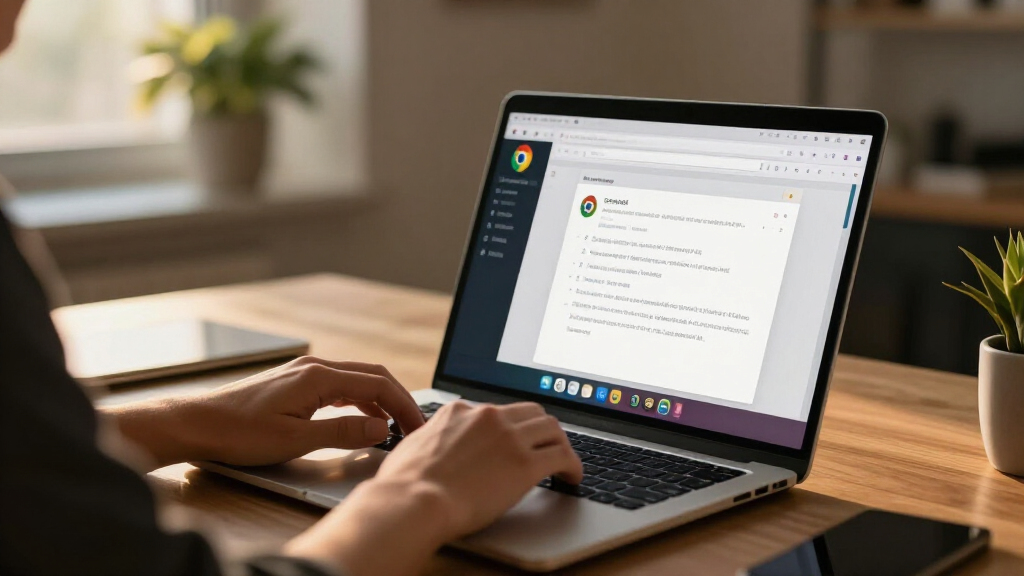
Google addressed a higher volume of Chrome bugs in June than in the previous two years, with AI playing a key role in identifying and fixing vulnerabilities. This marks a significant shift in browser security efforts.
Google fixed more security bugs in Chrome during June 2024 than in any month over the past two years, according to official reports. This achievement is attributed to the integration of artificial intelligence tools into the bug detection and fixing process, marking a major shift in the company’s approach to browser security.
Google’s Chrome security team reported that in June 2024, they resolved more vulnerabilities than in any previous month since mid-2022. The number of bugs fixed exceeded the total for the entire past two-year period, a milestone attributed directly to the deployment of AI-based analysis tools.
Google officials confirmed that AI algorithms helped identify potential security flaws more rapidly and accurately, enabling quicker development of patches. The company emphasized that this approach has improved both the efficiency and scope of their security efforts, especially in addressing zero-day vulnerabilities.
Implications of AI-Driven Bug Fixing for Browser Security
This development demonstrates how AI can significantly enhance cybersecurity efforts, especially in rapidly identifying and patching vulnerabilities. For users, it suggests a potential increase in browser security and a reduction in exploitable flaws. For the industry, it highlights a shift toward AI-assisted security workflows, which could influence how other software providers manage vulnerabilities.
However, the reliance on AI also raises questions about transparency, potential false positives, and the need for ongoing human oversight to ensure the accuracy of bug detection and fixing processes.
As an affiliate, we earn on qualifying purchases.
Background of Chrome Security and AI Adoption
Google Chrome has been a frequent target for security researchers due to its widespread use and complex codebase. Over the past two years, the company has steadily increased its bug bounty and security review efforts. In 2024, Google announced plans to incorporate AI tools into their security workflows, aiming to accelerate vulnerability detection.
Prior to June 2024, Chrome’s bug fixing pace was steady but not exceptional, with most vulnerabilities identified through manual review and traditional automated tools. The June milestone marks the first major impact of AI integration on bug resolution rates.
“The integration of AI has transformed our ability to identify and address vulnerabilities more efficiently than ever before.”
— Google Security Team Lead
As an affiliate, we earn on qualifying purchases.
Uncertainties Around AI’s Role and Future Effectiveness
While Google reports a significant increase in bug fixes, it is not yet clear how much of this is directly attributable to AI versus traditional methods. The long-term reliability and accuracy of AI-driven bug detection remain under evaluation, and there are ongoing discussions about potential false positives or overlooked vulnerabilities.
Additionally, the precise scale of AI’s contribution relative to manual review processes has not been publicly detailed, leaving some questions about how integrated AI truly is within their security workflow.
As an affiliate, we earn on qualifying purchases.
Next Steps for Google and Industry Adoption of AI in Security
Google plans to continue expanding its use of AI tools in Chrome security and will monitor the effectiveness of this approach over the coming months. The company may also share more detailed metrics on AI’s impact and work on improving the transparency of its processes.
Other browser and software developers are likely to observe this development closely, potentially adopting similar AI-driven security measures if results prove sustainable. Ongoing research and development in AI security tools will shape the future landscape of cybersecurity efforts across the industry.
As an affiliate, we earn on qualifying purchases.
Key Questions
How many bugs did Google fix in June 2024 compared to previous months?
Google fixed more bugs in June 2024 than in any month over the past two years, although exact numbers have not been publicly disclosed.
What role did AI play in fixing these bugs?
Google officials attribute the increased bug fixes to AI tools that helped identify vulnerabilities more quickly and accurately, enabling faster patching.
Are there concerns about relying on AI for security?
Yes, experts caution that AI’s effectiveness depends on transparency, avoiding false positives, and maintaining human oversight to verify findings.
Will this lead to more secure browsers overall?
If AI continues to improve bug detection and fixing, it could lead to more secure browsers and software, but long-term results are still being evaluated.
What does this mean for other software companies?
Other companies may adopt AI-driven security workflows if Google’s results demonstrate clear benefits, potentially transforming industry standards.
Source: hn
Fall Picks
fall essentials
As an affiliate, we earn on qualifying purchases.